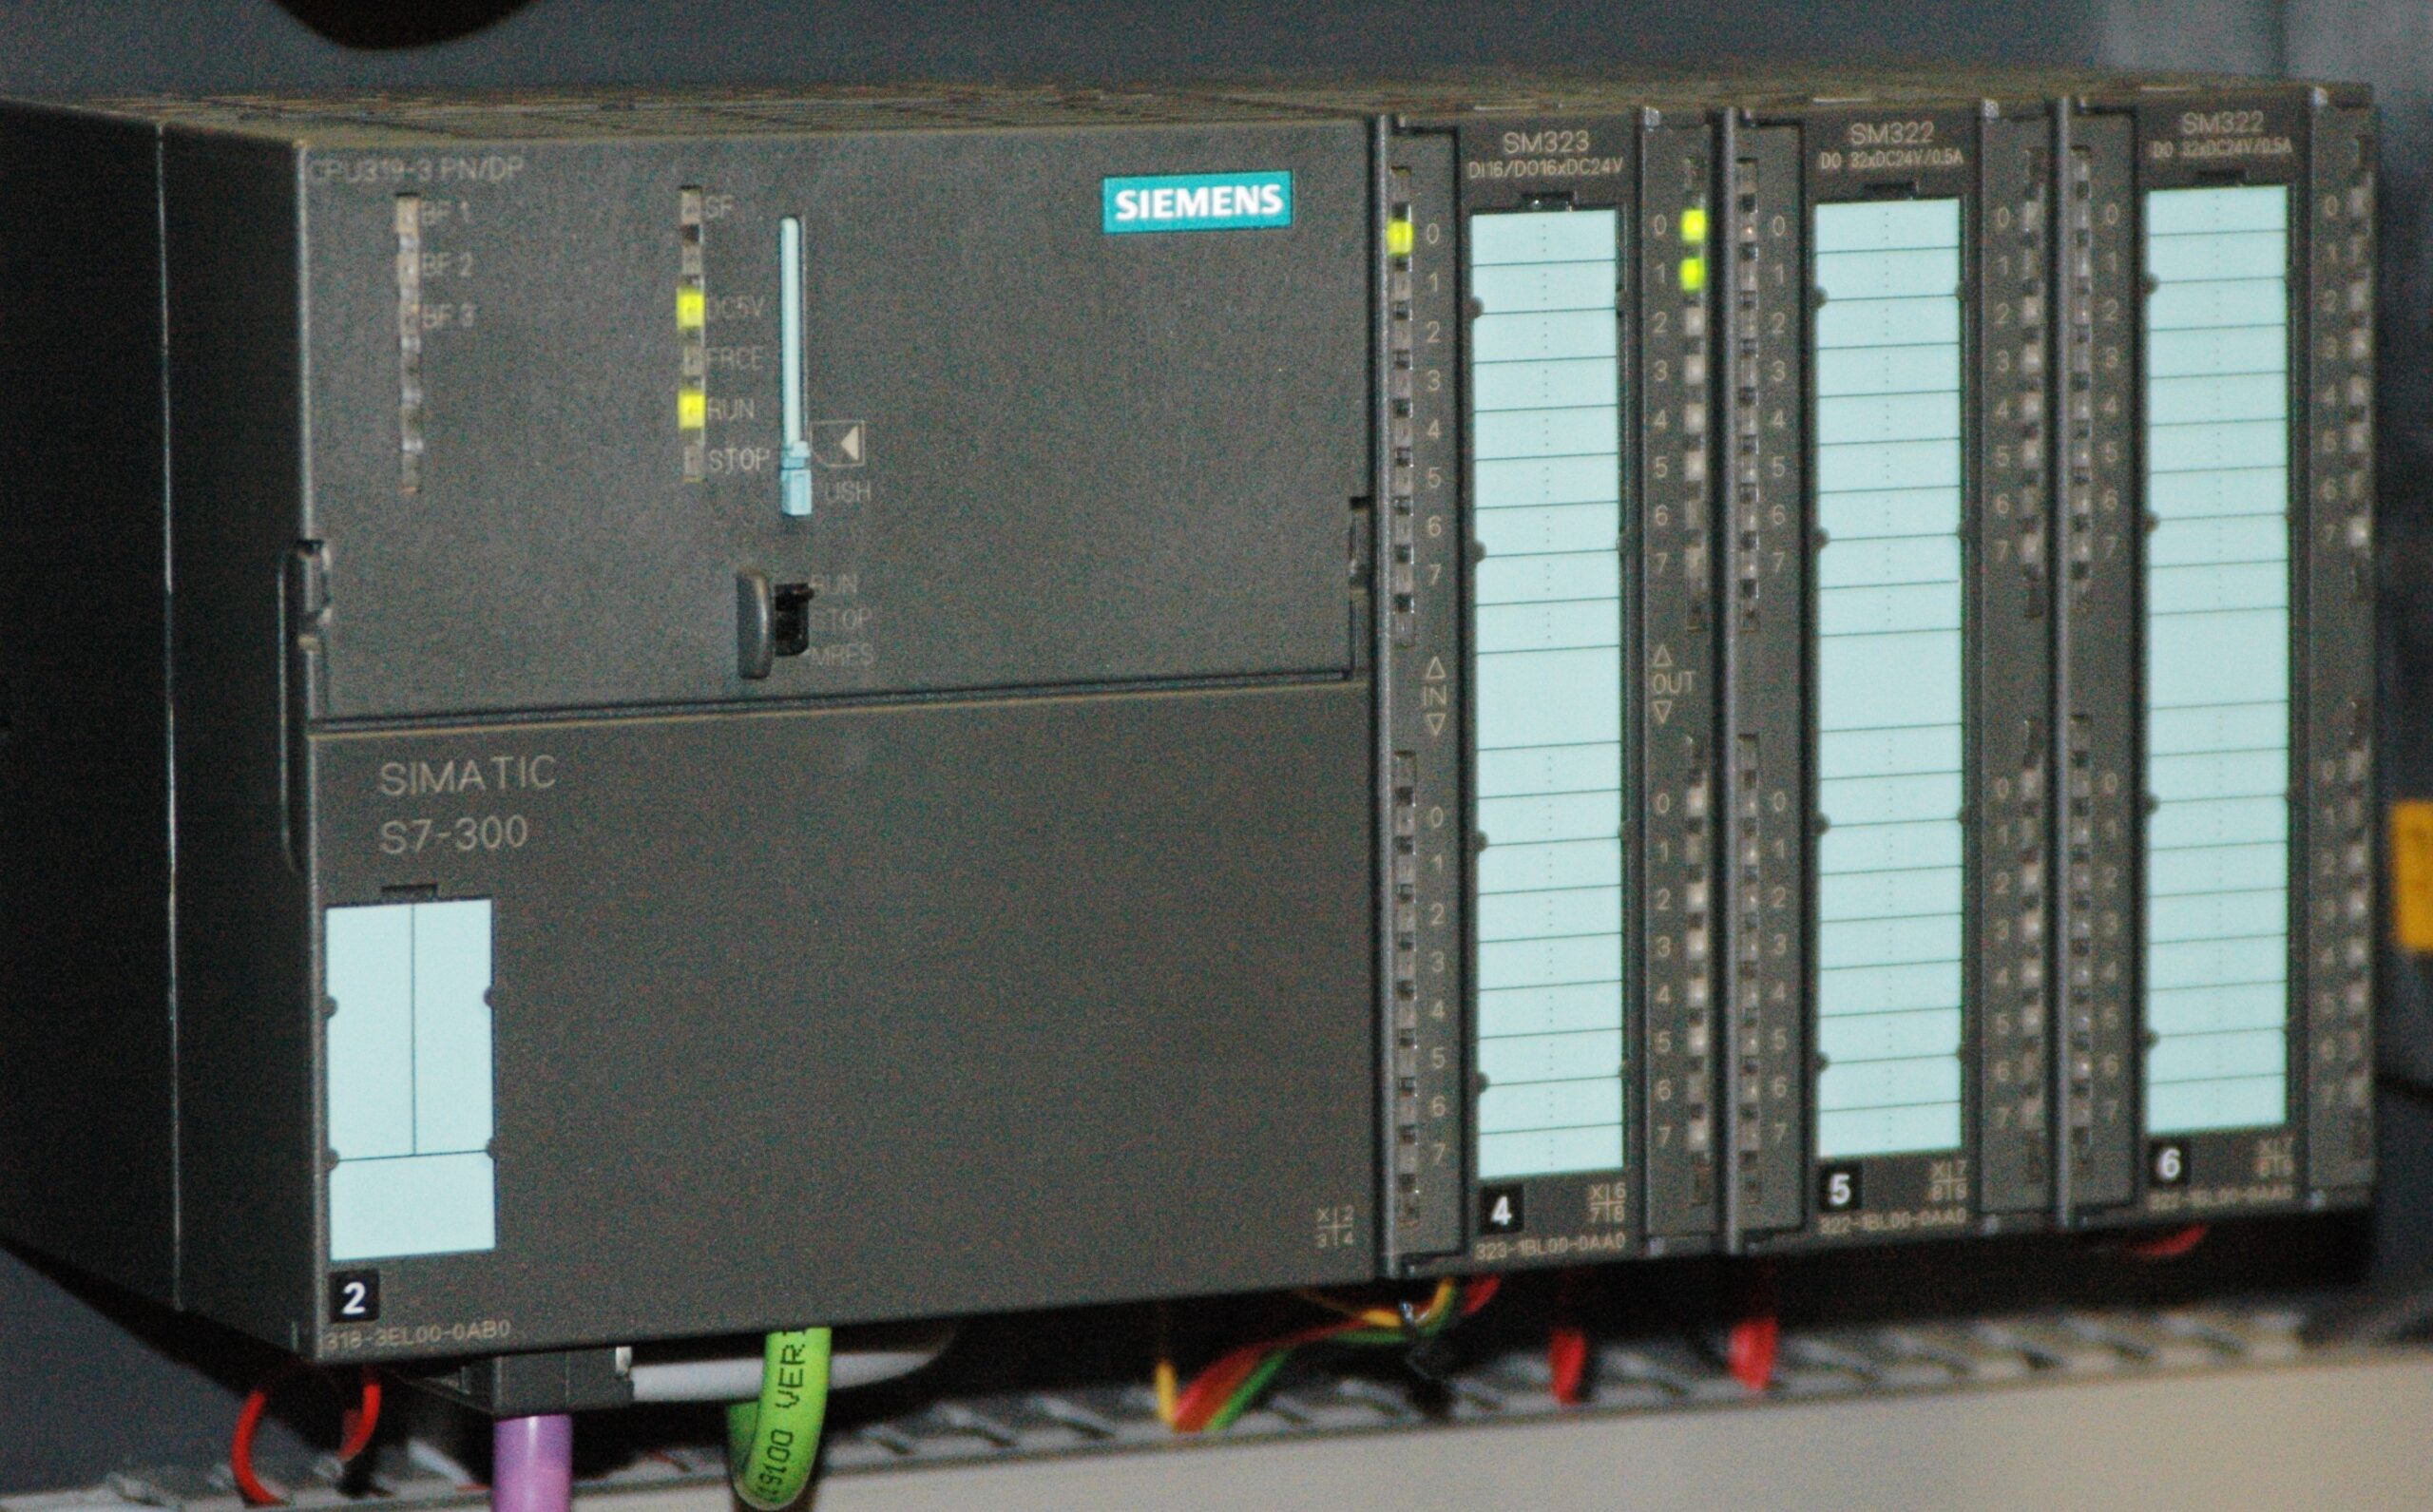
Cover image: Siemens SIMATIC S7-300 industrial programmable controller, photographed by Ulli1105; representative equipment, not a photograph of the Natanz facility. Original photograph, CC BY-SA 2.5; resized for this site.

Strategic Snapshot
Stuxnet remains one of the most important historical cases in cyber-physical security because it demonstrated that malicious software could be designed not merely to compromise computers, but to influence an industrial process.
Discovered publicly in 2010, the malware targeted Siemens industrial-control environments and used multiple pathways to reach engineering systems. Technical analysis shows that its industrial payload was highly selective and designed around specific control configurations associated with centrifuge operations at Iran's Natanz facility.
Three Key Takeaways
1. Cyber operations can produce physical effects.
Stuxnet demonstrated that malware could move from information systems into operational technology and alter the behavior of industrial equipment.
2. Precision depends on intelligence.
The malware's selective targeting indicates that detailed knowledge of equipment, process conditions, and industrial architecture was central to the operation.
3. Isolation is not absolute.
USB devices, engineering workstations, contractors, vendors, project files, and maintenance activities can create pathways into networks that are otherwise separated from the internet.
Why It Matters
The Stuxnet case remains relevant because modern infrastructure still depends on operational technology.
Power systems, manufacturing facilities, water infrastructure, transportation, logistics, and defense-industrial networks all rely on digital systems that interact with physical processes.
The deeper lesson is about trust.
Organizations need confidence not only that their networks are secure, but that the software controlling equipment and the information displayed to operators are accurate.
Read The Full Article
Read the full Stuxnet analysis
Recommended Resource
MITRE ATT&CK — Stuxnet (S0603) MITRE ATT&CK — Stuxnet (S0603)
More briefs coming soon, stay sharp.
Read more at https://www.thestrategiccurrent.com and follow The Strategic Current across all platforms.